What is Checkov?
Checkov is an open-source static code analysis tool for infrastructure-as-code (IaC). It scans configurations like Terraform, Kubernetes, and CloudFormation to find security and compliance misconfigurations, allowing teams to 'Shift Left' and secure their cloud resources before deployment.
In the fast-paced world of 2026, security cannot afford to be a bottleneck.
As organizations increasingly adopt "Shift Left" security practices, tools like Checkov are no longer optional—they are a core component of the modern CI/CD pipeline. Whether you are managing massive Terraform deployments, complex Kubernetes clusters, or multi-cloud CloudFormation templates, Checkov provides the visibility and enforcement needed to maintain a robust security posture.
What is Checkov?
Checkov is an open-source static code analysis tool for infrastructure-as-code. It scans cloud infrastructure configurations to find security and compliance misconfigurations. Created by Bridgecrew (now part of Palo Alto Networks), it has become one of the most popular tools in the DevSecOps ecosystem due to its broad support for various IaC frameworks and its extensive library of built-in policies.
Checkov analyzes the code itself to detect issues such as unencrypted storage buckets, overly permissive IAM roles, and publicly accessible databases long before any actual resources are provisioned in the cloud.
Key Takeaways
- Open-source tool for static analysis of IaC configurations.
- Supports Terraform, Kubernetes, CloudFormation, Helm, and more.
- Helps prevent security misconfigurations early in the development lifecycle.
Why IaC Security Scanning is Critical in 2026
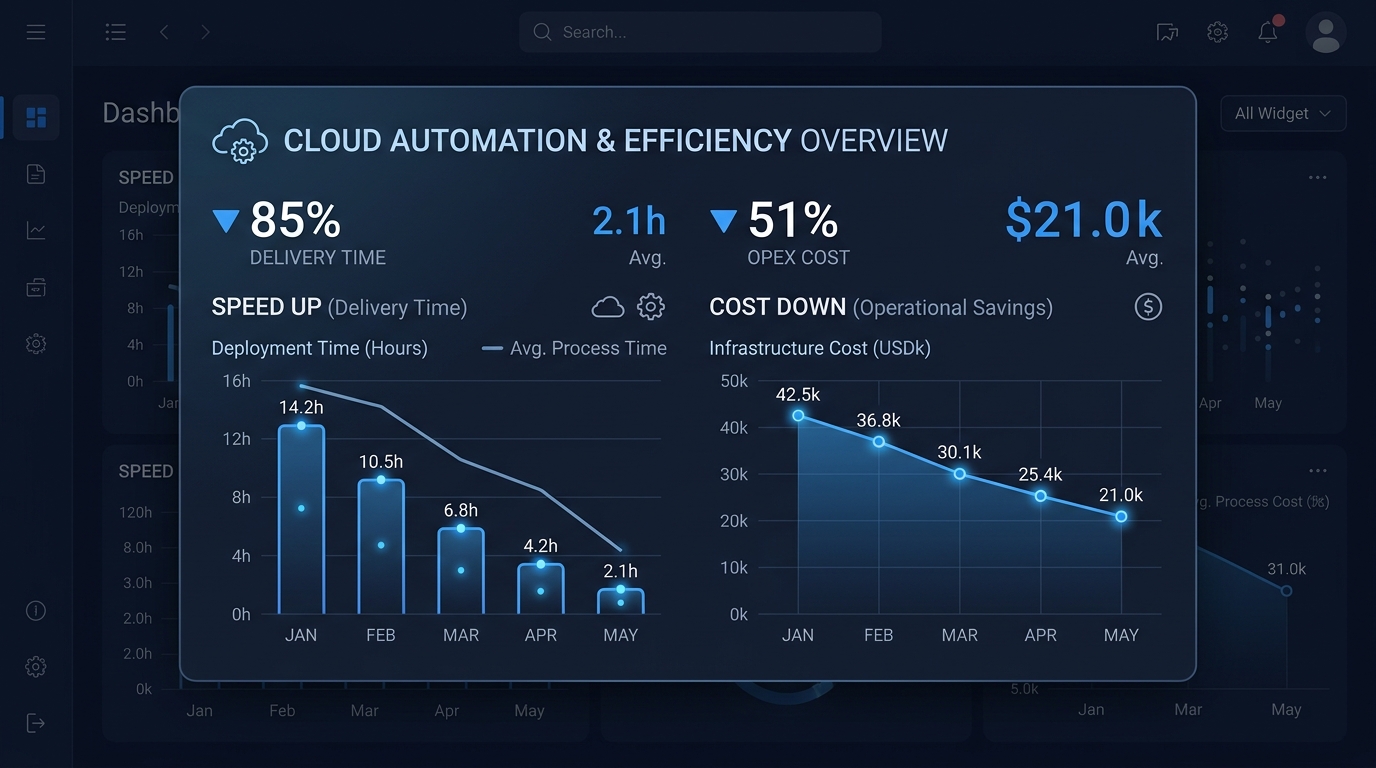
In 2026, the complexity of cloud environments has reached a point where manual security reviews are impossible. A single line of misconfigured code can expose sensitive data or lead to a costly security breach. **IaC security** is about preventing these issues at the source.
Policy as Code
Enforce security rules through code instead of manual checklists, ensuring consistent compliance across all environments.
Shift Left
Catch security flaws in the development phase, significantly reducing the cost and complexity of remediation.
Auto-Remediation
Checkov can suggest or apply automated fixes, empowering developers to maintain a secure posture effortlessly.
Key Features of Checkov
Checkov isn't just a simple linter; it's a comprehensive security platform. Its features in 2026 have evolved to meet the needs of the most demanding enterprise environments.
- 1000+ Built-in Policies: Covers best practices for AWS, Azure, GCP, and Kubernetes based on CIS benchmarks.
- Custom Policy Support: Write your own rules using YAML or Python for organization-specific requirements.
- Graph-based Analysis: Understands complex resource relationships for context-aware security checks.
- Broad Framework Support: Works with Terraform, CloudFormation, Helm, ARM, Bicep, and Dockerfiles.
Comparison: Checkov vs. Terrascan vs. TFLint
Choosing the right **Terraform security scanner** is essential for a robust security pipeline.
| Feature | Checkov | Terrascan | TFLint |
|---|---|---|---|
| Primary Focus | Security & Compliance | Security & Compliance | Syntax & Logic |
| Frameworks | Multi-IaC (10+) | Multi-IaC (5+) | Terraform Only |
| Policy Language | YAML / Python | Rego (OPA) | HCL / Custom |
| Graph Analysis | Yes | Limited | No |
| Ideal For | DevSecOps Teams | OPA-centric Teams | Linting & Standards |
Step-by-Step: Installing and Using Checkov
Install via pip or brew and start scanning your infrastructure in seconds.
# Install Checkov
pip install checkov
# Run a scan on the current directory
checkov -d .
Checkov will provide a clear pass/fail status for each policy, along with a description of the issue and a link to the documentation for the fix.
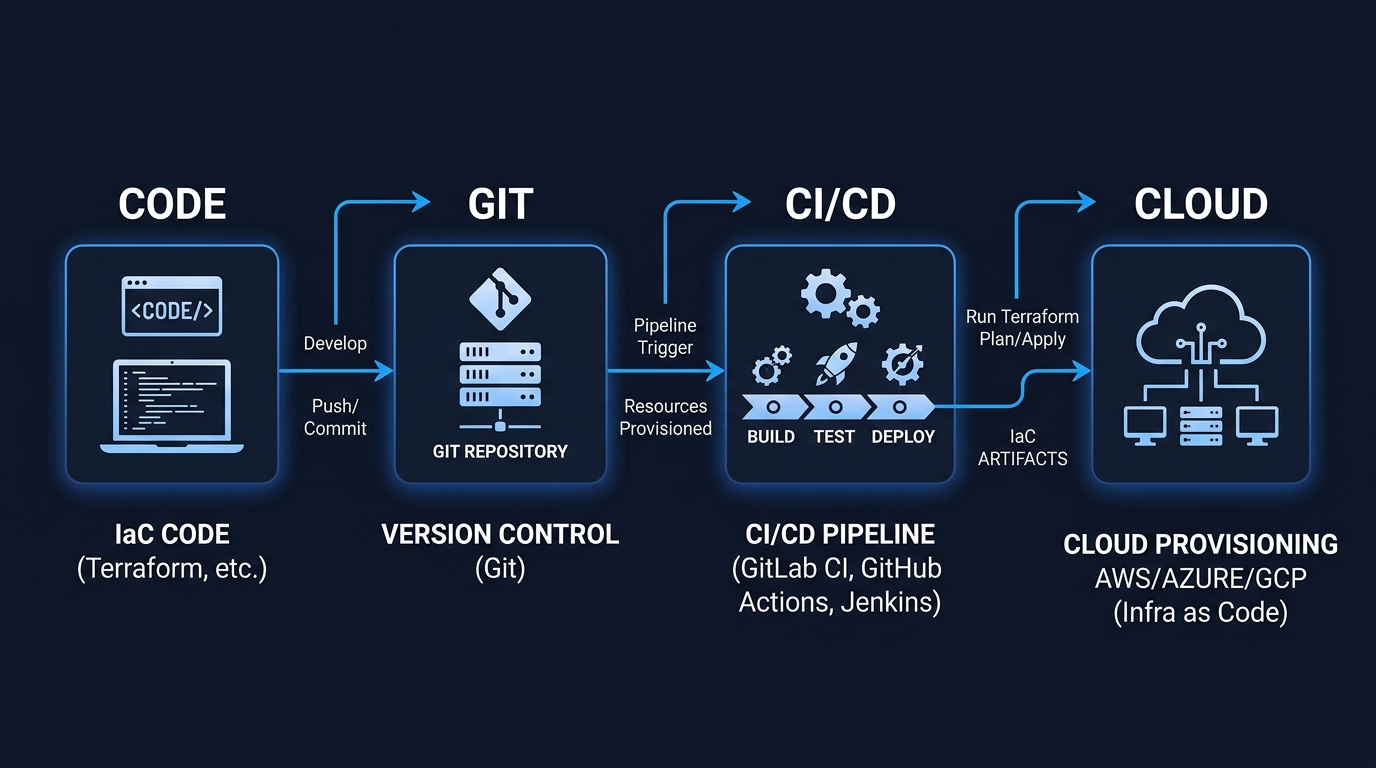
Integrating Checkov into CI/CD Pipelines
Pro Tip: Pipeline Automation
Use the official Checkov GitHub Action to automatically scan every Pull Request. Set threshold levels to fail builds only on high or critical vulnerabilities.
Conclusion
In 2026, **static analysis for IaC** is a cornerstone of a secure cloud strategy. Checkov provides the perfect balance of power, flexibility, and ease of use, making it an essential tool for any team serious about cloud security.
At UseShift, we help organizations implement cutting-edge DevSecOps practices. Contact UseShift today for a technical audit of your automation and security pipelines.
Key Takeaways
- Checkov is the gold standard for multi-framework IaC security scanning.
- Enables 'Shift Left' security by catching misconfigurations early.
- Seamless integration into modern CI/CD pipelines.
- Comprehensive support for both built-in and custom security policies.